Pie Register Premium through 3.8.4.0 – Actively Exploited Unauthenticated File Upload (CVE-2026-84999)

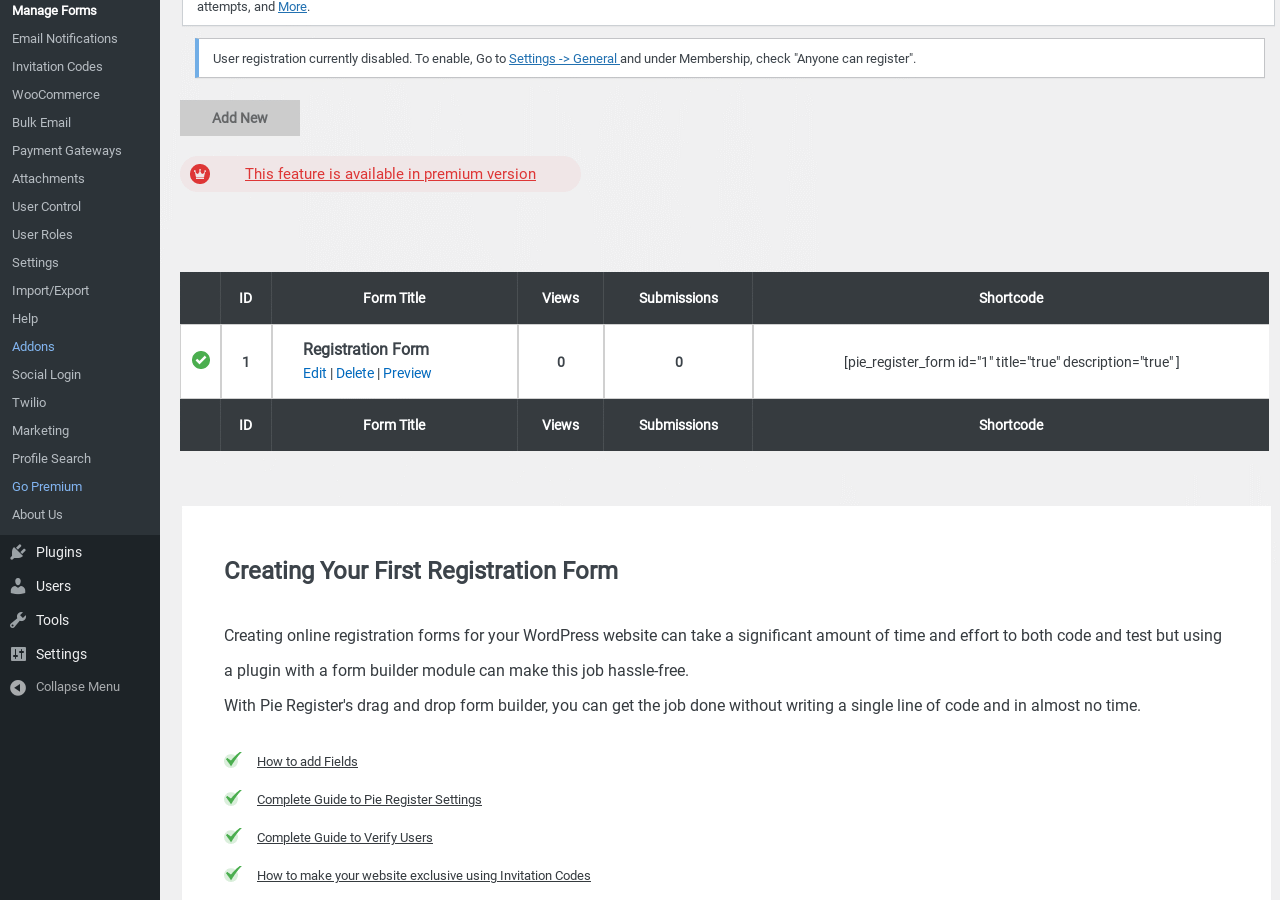
Pie Register Premium versions 3.8.4.0 and earlier contain a critical unauthenticated arbitrary file upload vulnerability tracked as CVE-2026-84999. Patchstack lists the flaw as actively exploited. Update to 3.8.4.1 or later immediately and investigate vulnerable sites for uploaded backdoors.
| Product | Pie Register Premium |
|---|---|
| Affected versions | 3.8.4.0 and earlier |
| Fixed version | 3.8.4.1 |
| CVE | CVE-2026-84999 |
| Severity | Critical, CVSS 9.8 |
| Authentication | Not required |
| Attack class | Unrestricted file upload leading to possible remote code execution |
| Exploitation | Active exploitation reported by Patchstack |
How the vulnerability works
According to Wordfence, the public AJAX handler piereg_file_upload calls WordPress file-type validation functions but does not stop processing when those checks report an error. The handler also lacks a nonce check and capability check before moving the uploaded file.
An unauthenticated attacker can therefore upload a dangerous file type. On configurations where uploaded PHP files are executable, this can become remote code execution. The response discloses the generated destination filename, removing the need for an attacker to guess where the file was stored.
Immediate remediation
- Update Pie Register Premium to version 3.8.4.1 or later using the vendor’s authenticated update channel.
- If the update cannot be applied immediately, deactivate Pie Register Premium and block public access to its upload AJAX action at the WAF or reverse proxy.
- Review web logs for requests involving
piereg_file_upload, especially successful responses and follow-up requests to newly created files. - Search writable upload directories for executable files and investigate any unexpected additions.
- Review administrator accounts, active plugins, scheduled tasks, and outbound connections. Rotate WordPress salts, administrator passwords, hosting credentials, database credentials, and API keys if compromise is suspected.
Verify the installed version
wp plugin get pie-register-premium --fields=name,status,version,update,update_version
wp plugin list --fields=name,status,version,update --format=table
wp user list --role=administrator --fields=ID,user_login,user_email,user_registered --format=table
wp cron event list --fields=hook,next_run_gmt,recurrence --format=table
wp core verify-checksums
Because this is a premium plugin, an automatic WP-CLI update may require an active license and the vendor updater. Confirm the final installed version is 3.8.4.1 or newer.
Indicators to review
- Unauthenticated requests to the Pie Register upload AJAX handler.
- Unexpected PHP or executable files below
wp-content/uploadsor other writable directories. - HTTP requests to files created shortly after an upload request.
- New administrator users, unfamiliar plugins, changed options, unknown cron hooks, or modified PHP files.
Do not treat a successful update as proof that the site was not compromised. If a vulnerable version was publicly reachable during the exploitation window, preserve logs, remove malicious files only after collecting evidence, restore from a known-good backup when appropriate, and rotate reachable secrets.
Sources
